
CO-MANAGED CYBERSECURITY
Co-Managed Cybersecurity Services
Expand your cybersecurity capabilities. Build on the IT support that works.
IT Assure delivers Cyber Defensibility alongside your current IT resources—managing agreed protections, validating coverage monthly, and correcting routine security gaps.
Your firm gains support for covered cybersecurity work, with clear reporting for IT and leadership.
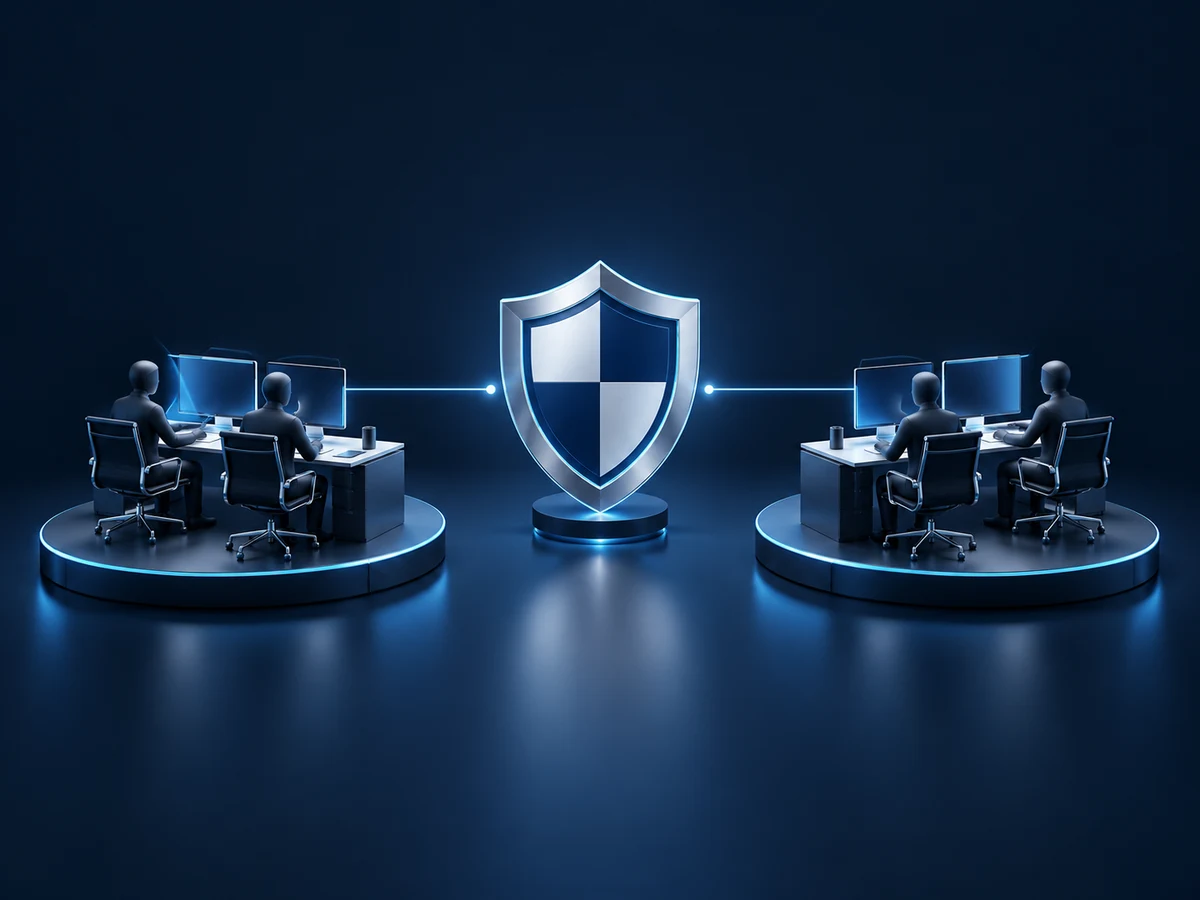
WHERE CO-MANAGED FITS
Stronger cybersecurity.
Support for the team you have.
Your internal IT team or current provider may keep technology running well. Co-managed cybersecurity can add capability or capacity where security work needs more attention.
We compare your existing protections and responsibilities with our defined service to identify useful additions and any overlap.
Your IT works. Security needs more attention.
Keep effective IT support and add management for agreed security protections.
Your team is stretched thin.
Give routine covered cybersecurity work a dedicated service alongside daily IT.
You need consistent follow-through.
Check intended coverage, correct routine gaps, and verify the result.
You need clearer accountability.
See who handles the work, what was corrected, and which decisions remain.

If your current team covers this work effectively, an additional service may add little value. Compare managed IT and managed cybersecurity →
HOW WE WORK TOGETHER
What we manage.
How we work with your IT team.
Your existing resources continue supporting daily IT. We manage agreed cybersecurity protections, with clear handoffs when work overlaps.
Read across each row to see the division of work. On smaller screens, swipe the table to see all columns.
| RESPONSIBILITY AREA |
Your IT / your firmYOUR PEOPLE, YOUR BUSINESS
|
TogetherCOORDINATION & HANDOFFS
|

IT AssureCOVERED CYBERSECURITY WORK
|
|---|---|---|---|
 Daily IT support |
Primary responsibilityEmployees, applications, and daily technology.
|
Coordinate as neededShare findings affecting daily IT.
|
Security findingsWork within the cybersecurity scope.
|
 Users & devices |
Communicate changesProvide the roster and access decisions.
|
Confirm coverageAgree the users, devices, and access.
|
Verify protectionsCheck required security coverage.
|
|
Security controls |
Access & participationAdopt required protections.
|
Coordinate changesConfirm tools and implementation needs.
|
Manage & validateMaintain agreed controls and coverage.
|
 Routine security gaps |
Authorize covered workProvide the agreed access and authority.
|
Coordinate affected workAlign changes with existing resources.
|
Correct & recheckFix routine covered gaps; verify results.
|
 Reporting & decisions |
Review & approveMake business decisions; approve extra work.
|
Agree next actionsResolve outstanding decisions together.
|
Report & recommendShow checks, corrections, and next steps.
|
The exact division of work is agreed before service begins. This is an illustrative map. Your agreement defines covered systems, access, response authority, and included work. Additional projects, remediation, and business-impacting changes outside preapproved authority require a scope or approval decision.
WHAT WE MANAGE
Agreed protections.
Routine work handled for your firm.
Our standard Cyber Defensibility service manages the controls below, checks intended coverage monthly, corrects routine covered gaps, and reports the results.
MFA & identity protection
 Endpoint threat detection
 Email security & training
 Patches & encryption
 Backup coverage checks
Validation, correction & reporting
Your agreement identifies covered users, devices, systems, and applicable controls. We confirm access and any required tool changes with your existing resources. Limited customization is subject to approval and may carry different pricing. See the full Cyber Defensibility service →
What does your team need to do?
Provide access, keep staff and device information current, and make the business decisions and approvals the service needs.
Getting started: onboarding usually completes within 30 days of starting, with a few hours of coordination.
Typical ongoing participation: about 10 minutes per monthly report and around one hour for scheduled reviews, quarterly or twice yearly as agreed. Timing depends on your environment, access, provider coordination, and additional remediation. Incidents, projects, employee security steps, and approvals may need more involvement. See onboarding and participation details →
YOUR NEXT STEP
Explore how your cybersecurity capabilities could expand.
In an approximately 30-minute Cybersecurity Review, discuss your current coverage, the work you want handled, and whether our defined service fits.
Your IT representative is welcome to join. Any technical validation is a separate step.
 A useful first conversation

Explain your current protections and working arrangements.
Discuss the capabilities you want to strengthen.
Identify service fit and an appropriate next step.
No technical preparation required. No obligation to engage.
Prefer to start on your own? Take the Quick Self-Check →
The self-check reflects your answers; it is not technical validation.
Standard plans from $80 per seat/month · 10-seat minimum · Month-to-month service.
A one-time, non-refundable onboarding fee is quoted separately. Service-fee discounts apply for firms maintaining eligible cyber liability insurance; volume discounts may also be available. Your proposal confirms scope, final pricing, and terms. See pricing and conditions →