
CYBER DEFENSIBILITY FOR LAW FIRMS
Cybersecurity for Law Firms
Protect the information your clients
trust you to keep private.
Client files, matter documents, and confidential correspondence move through the accounts and devices your team uses every day.
IT Assure delivers Cyber Defensibility: managed cybersecurity that maintains agreed protections, verifies coverage monthly, and corrects routine security gaps.
 Client confidentiality
 Attorney & staff devices
 Coverage verified monthly
CONFIDENTIALITY & FOLLOW-THROUGH
Safeguarding client information
requires ongoing attention.
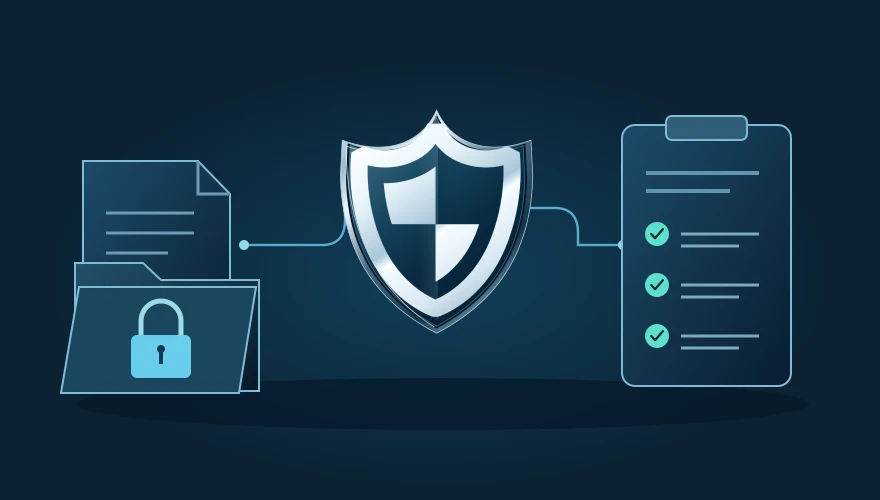
Professional confidentiality responsibilities, practical cybersecurity safeguards, and a clear process for addressing concerns all matter.
Client confidentiality
Your firm determines matter access and fulfills its professional responsibilities.
Security safeguards
IT Assure manages and verifies the agreed technical protections.
Accountability
Findings are documented, corrected when covered, or escalated for a decision.
Monthly reporting shows coverage, completed corrections, remaining actions, and decisions needed. We also provide relevant technical information about managed controls for client security and cyber-insurance questions. Your firm and advisers retain responsibility for professional, contractual, and insurance representations.
PROTECTIONS & PERMISSIONS
Protect accounts. Make
matter-access decisions explicit.
Protecting an account and deciding which client matters it may access are connected responsibilities. We make the division of work clear.
Your law firm
MATTER-ACCESS DECISIONS
- Who may access each matter
- Approved permissions
- Authorization for changes
IT Assure
AGREED ACCOUNT PROTECTIONS
- Required account MFA
- Identity threat monitoring
- Covered device protection
Matter applications
ACCESS IN THE SYSTEMS YOU USE
- Confirm application scope
- Coordinate provider access
- Approve broader work
Your firm sets matter-access decisions. IT Assure manages agreed technical protections. Application changes, broader permissions work, and provider involvement follow the agreed scope and required authorization.
WHAT WE MANAGE
Law firm cybersecurity services
Agreed protections, actively managed around your firm’s covered environment.
Monthly validation compares intended coverage with actual protection. We correct routine covered gaps, recheck, and report the work. Your agreement identifies covered users, devices, systems, and controls. Explore the complete Cyber Defensibility service →
BUILD ON WHAT WORKS
Keep effective IT support.
Make security responsibilities clear.
We work alongside your current IT and legal-application resources, with clear handoffs when the work overlaps.
Read across each row. On smaller screens, swipe the table to see all columns.
| Responsibility | Your firm & existing resources | Together | IT Assure |
|---|---|---|---|
 Matter access |
Decide and approve who may access client matters. | Confirm application ownership and access needed. | Manage agreed account protections and report concerns. |
| Daily IT & legal applications |
Retain daily IT and application support arrangements. | Coordinate findings that affect client work. | Handle cybersecurity work within the covered scope. |
 Security gaps |
Provide agreed access and authorize covered corrections. | Align changes with affected providers. | Correct routine covered gaps and verify the result. |
| Reporting & decisions |
Review findings and approve additional work. | Agree outstanding actions and responsibilities. | Report checks, corrections, and recommended next steps. |
Coverage for practice-management systems, document platforms, client portals, and vendor-hosted data is established individually. Explore the co-managed service →
GETTING STARTED
Coordinate onboarding
around client work.

Plan around client work
Discuss hearings, filing deadlines, closings, access, and provider coordination.

Establish initial coverage
Bring agreed protections under management, verify coverage, and document remaining actions.
Continue the recurring work
Monitor, validate, correct routine covered gaps, and report.
Typical management participation includes a few hours of onboarding coordination. Timing depends on your environment, access, provider coordination, and additional remediation. Employee security steps, approvals, scheduled reviews, incidents, and projects may require additional involvement. Review the process and participation expectations →
DISCUSS THE PROTECTION YOUR FIRM NEEDS
Start with your firm.
Find the right next step.
In an approximately 30-minute Cybersecurity Review, we discuss your working environment, current providers, and the capabilities you want strengthened.
Your people, accounts, and devices
Current IT and application arrangements
 What you need handled
No technical preparation required. No obligation to engage. Your IT representative is welcome. Any technical validation is a separate step.
WHAT YOUR FIRM GETS
Keep protections current.
Make the work visible.
PLANS START AT
$80 per seat / month
Keep coverage aligned as accounts and devices change
Get routine covered gaps corrected and rechecked
Know what was completed and what needs a decision
Compare Basic, Pro, and Premium →
10-seat minimum. Month-to-month service. A one-time, non-refundable onboarding fee is quoted separately. Service-fee discounts apply for eligible cyber liability insurance, subject to confirmation; volume discounts may be available. Your proposal defines scope, cancellation requirements, and any separately approved third-party commitments.