
CYBER DEFENSIBILITY FOR INSURANCE AGENCIES
Managed Cybersecurity
for Insurance Agencies
Protect policyholder information.
Keep your team focused on clients.
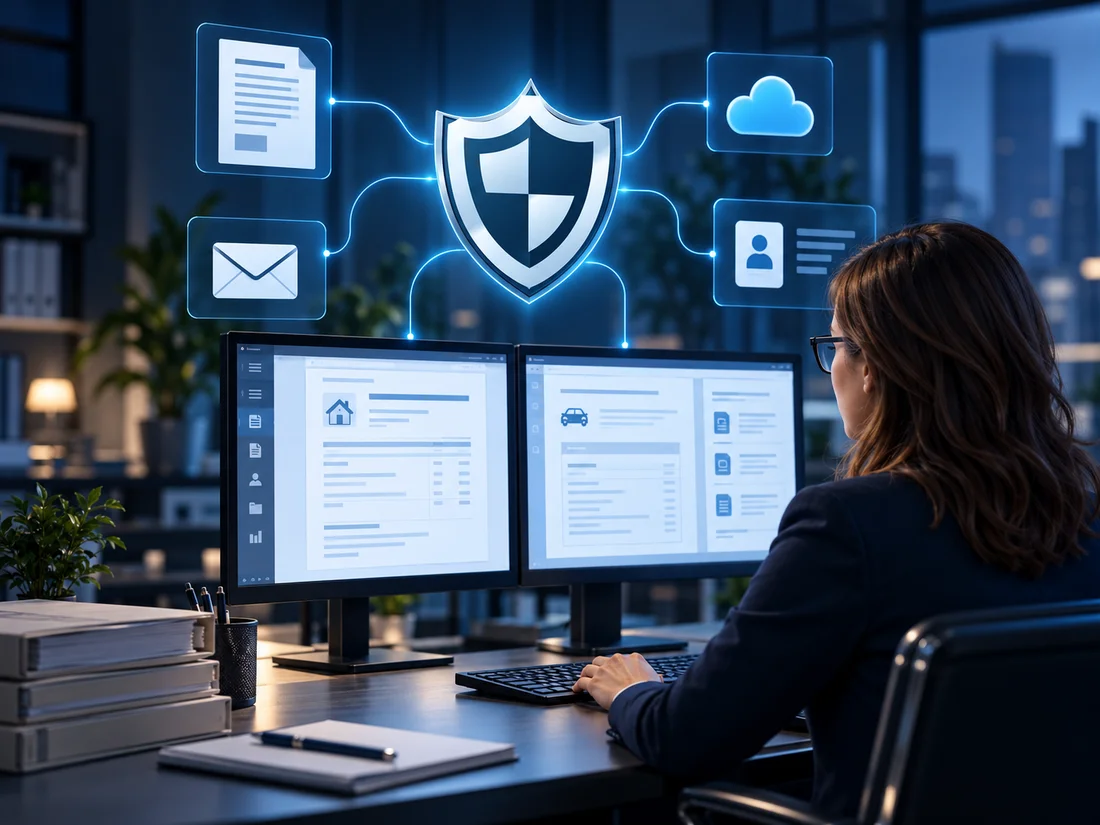
Applications, policy records, claims correspondence, and business email carry information your clients trust you to protect.
IT Assure manages agreed cybersecurity protections, verifies coverage monthly, and corrects routine covered gaps—alongside your current IT and agency-software resources.
Approximately 30 minutes. No technical preparation required. No obligation to engage.
 Policyholder information
 Protections checked monthly
 Completed work made visible
FOLLOW THROUGH ON PROTECTION GAPS
Installed tools are a starting point.
Actual coverage needs checking.
A producer joins. A laptop is replaced. A mailbox is added. The agency changes, and the intended protections need to keep up.
We compare the agreed roster and controls with what is actually operating, correct routine covered gaps, and verify the result.
| Covered environment | What should be in place | What the check finds |
|---|---|---|
 Staff accounts |
Required MFA and identity protections | Required MFA confirmed |
 Computers |
Endpoint protection, encryption, patches, and MDR | Replacement laptop: endpoint agent not reporting |
 Email & people |
Email defenses and security-awareness training | Agreed controls checked |
 Backup coverage |
Covered activity, failures, and intended systems | Intended coverage checked |
Safeguarding policyholder information is an ongoing responsibility.
Applicable insurance privacy rules can require a written information-security program with administrative, technical, and physical safeguards. California’s rules and Nevada’s rules provide examples.
IT Assure manages the agreed technical protections and records the work. Your agency and advisers determine the requirements that apply and retain responsibility for the broader program. The service does not certify compliance.
KEEP USEFUL SUPPORT IN PLACE
Keep agency operations and
security responsibilities clear.
Your staff, IT provider, and agency-software vendors may each handle part of the environment. We confirm how our defined cybersecurity service fits with their work.
Your agency
PEOPLE & BUSINESS DECISIONS
- Decide who should have access
- Communicate staff and device changes
- Provide access and timely approvals
IT Assure
AGREED CYBERSECURITY WORK
- Manage the covered protections
- Validate, correct, and recheck
- Report findings and recommended actions
IT & software providers
DAILY OPERATIONS & APPLICATIONS
- Support daily IT as agreed
- Maintain AMS, CRM, and carrier-platform functions
- Coordinate changes affecting security
AMS administration, application troubleshooting, integrations, and carrier-hosted systems are included only when expressly agreed. Explore co-managed cybersecurity →
GIVE LEADERSHIP A USEFUL VIEW
Know what was checked.
See what happened next.
Your monthly report shows the checks performed, findings, completed corrections, and remaining actions. Leadership can see the work without managing each security tool.
When a finding needs additional work or your approval, we explain the issue and recommend a next action.
Current technical information about the controls we manage can also support your agency’s own insurance and client-security discussions. Your agency remains responsible for its application answers; insurers make their own underwriting and coverage decisions.
 Checked
 Corrected
Typical estimates depend on access, your environment, provider coordination, and additional remediation. A few hours of onboarding coordination are usually needed. Scheduled reviews typically take around one hour, quarterly or twice yearly as agreed. Incidents, projects, employee security steps, and approvals can require more participation. See How It Works →
FOR AGENCIES & REFERRAL PARTNERS
Protecting your agency?
Helping a policyholder?
Start with the environment that needs attention. This page describes cybersecurity for your agency’s own accounts, devices, and systems.
For your own agency
Discuss the protections you want managed and how the service will fit with your current resources.
Referring a client
If a policyholder needs help with technical cybersecurity gaps, contact us to discuss their situation and referral fit.
CHOOSE A USEFUL FIRST STEP
Start with your agency’s
current situation.
Discuss your current arrangements and next steps, or start with seven self-check questions.

Cybersecurity Review
Discuss your current arrangements, concerns, and whether the service fits. Any technical validation is a separate step.
Approximately 30 minutes. No technical preparation required. No obligation to engage. Your IT representative is welcome.
Quick Self-Check
Consider who owns your cybersecurity work and how your agency checks coverage.
Seven questions. No meeting required. This is a self-check, not technical validation.
Managed cybersecurity plans start at $80 per seat/month, with a 10-seat minimum. Month-to-month service. A one-time, non-refundable onboarding fee is quoted separately. Your agreement defines scope, cancellation requirements, and separately approved third-party commitments. Compare plans and pricing →